

Architecting for Protection from Breach
How to Protect Your PII and Meet DPDP Requirements
Limit sensitive data exposure across systems and enforce DPDP-aligned control through data architecture.
What you'll walk away with:
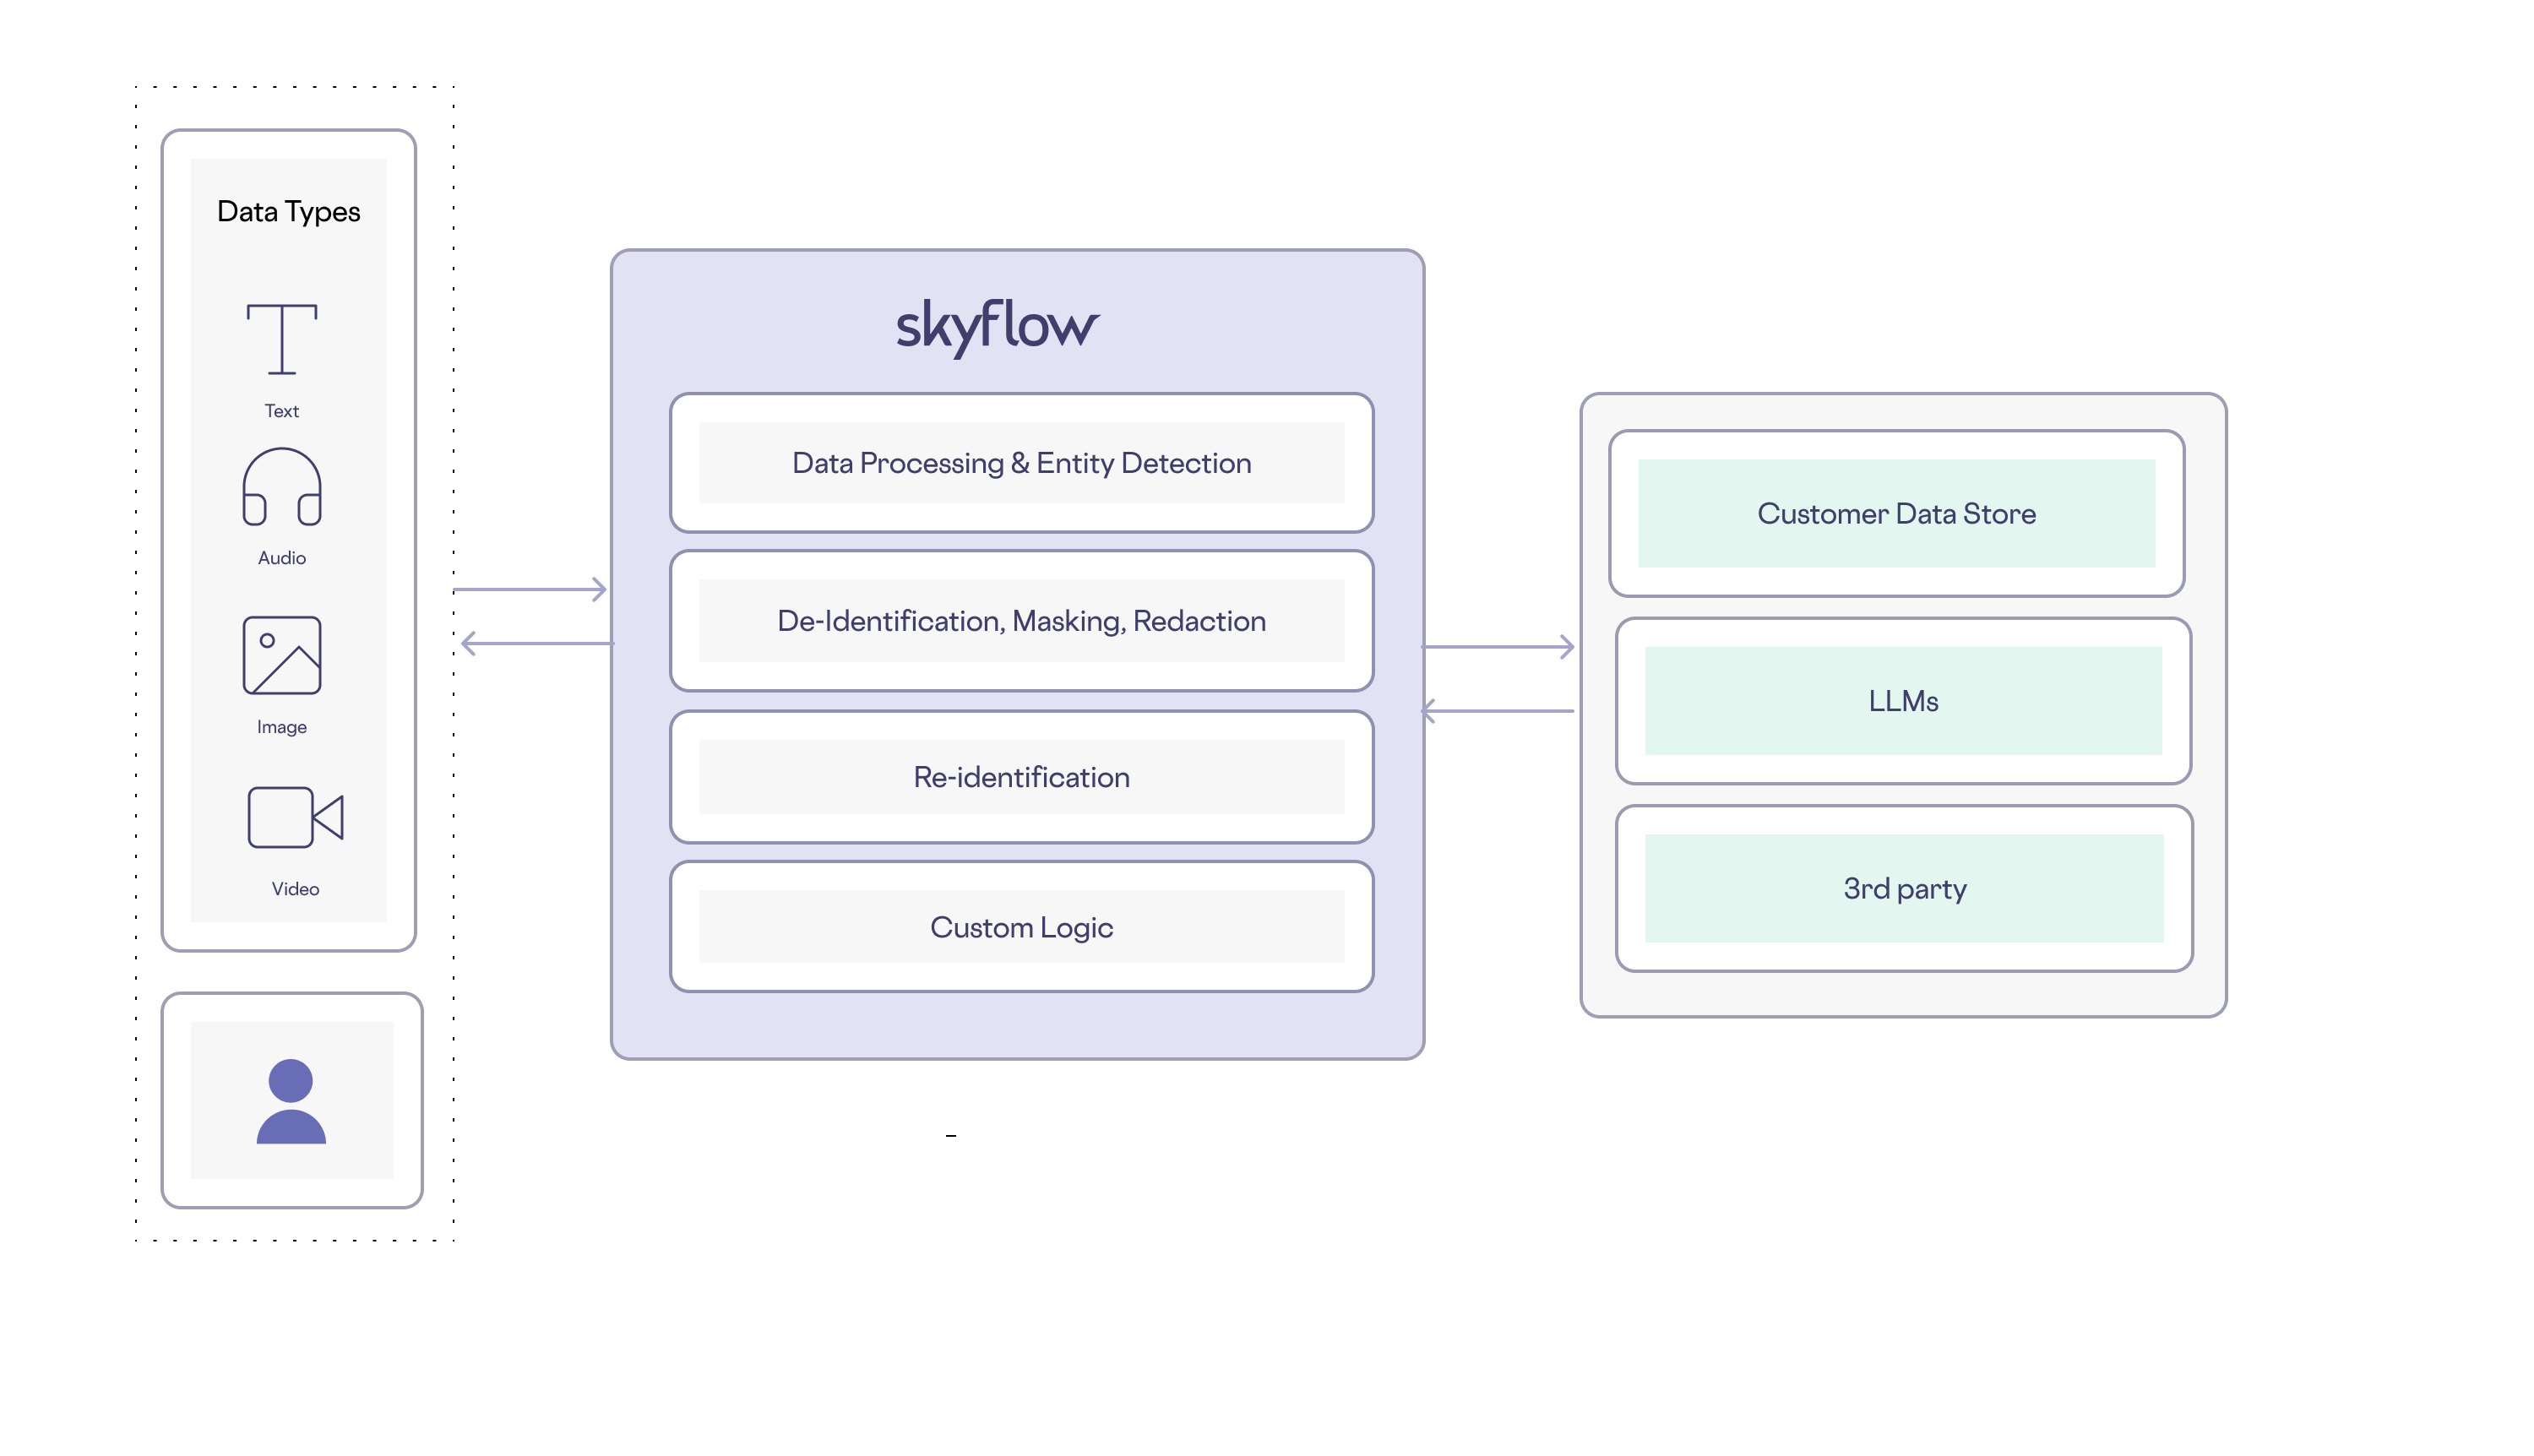
- A data architecture that reduces breach blast radius to near zero
- Runtime controls that secure sensitive data across every API touchpoint
- DPDP enforcement built into your execution layer, not just your policy docs
Complete the form below to register
What will you learn?
Join Daniel Wong, CISO at Skyflow, as he shares how leading security teams are going beyond perimeter defenses to protect PII at the data layer — reducing breach impact and simplifying DPDP compliance through architecture. You will learn:
How to reduce breach blast radius by limiting how much sensitive data is reachable across APIs, logs, and internal systems
How to strengthen your data security posture by layering architecture-level controls on top of existing defenses
How to move DPDP compliance from periodic reviews to automatic enforcement at the data layer
“We securely store and govern PII data efficiently, ensuring operational and engineering ease."


TRUSTED BY


Ready to Get Started?
Let us show you why Skyflow is the better way — sign up to talk to an expert today.