

Building for the EU AI Act
When an AI agent retrieves a customer record to generate a response, PII has already moved through the prompt, the agent context, the RAG retrieval, and the prompt log.
Under GDPR and the EU AI Act, the question isn't whether PII appears at each point. It's whether the agent actually needs the customer data to do its job.
You will learn:
- Where PII gets exposed in a modern AI stack, and what GDPR requires at each point
- The runtime pattern that keeps sensitive data out of prompts, context, and memory while preserving model accuracy
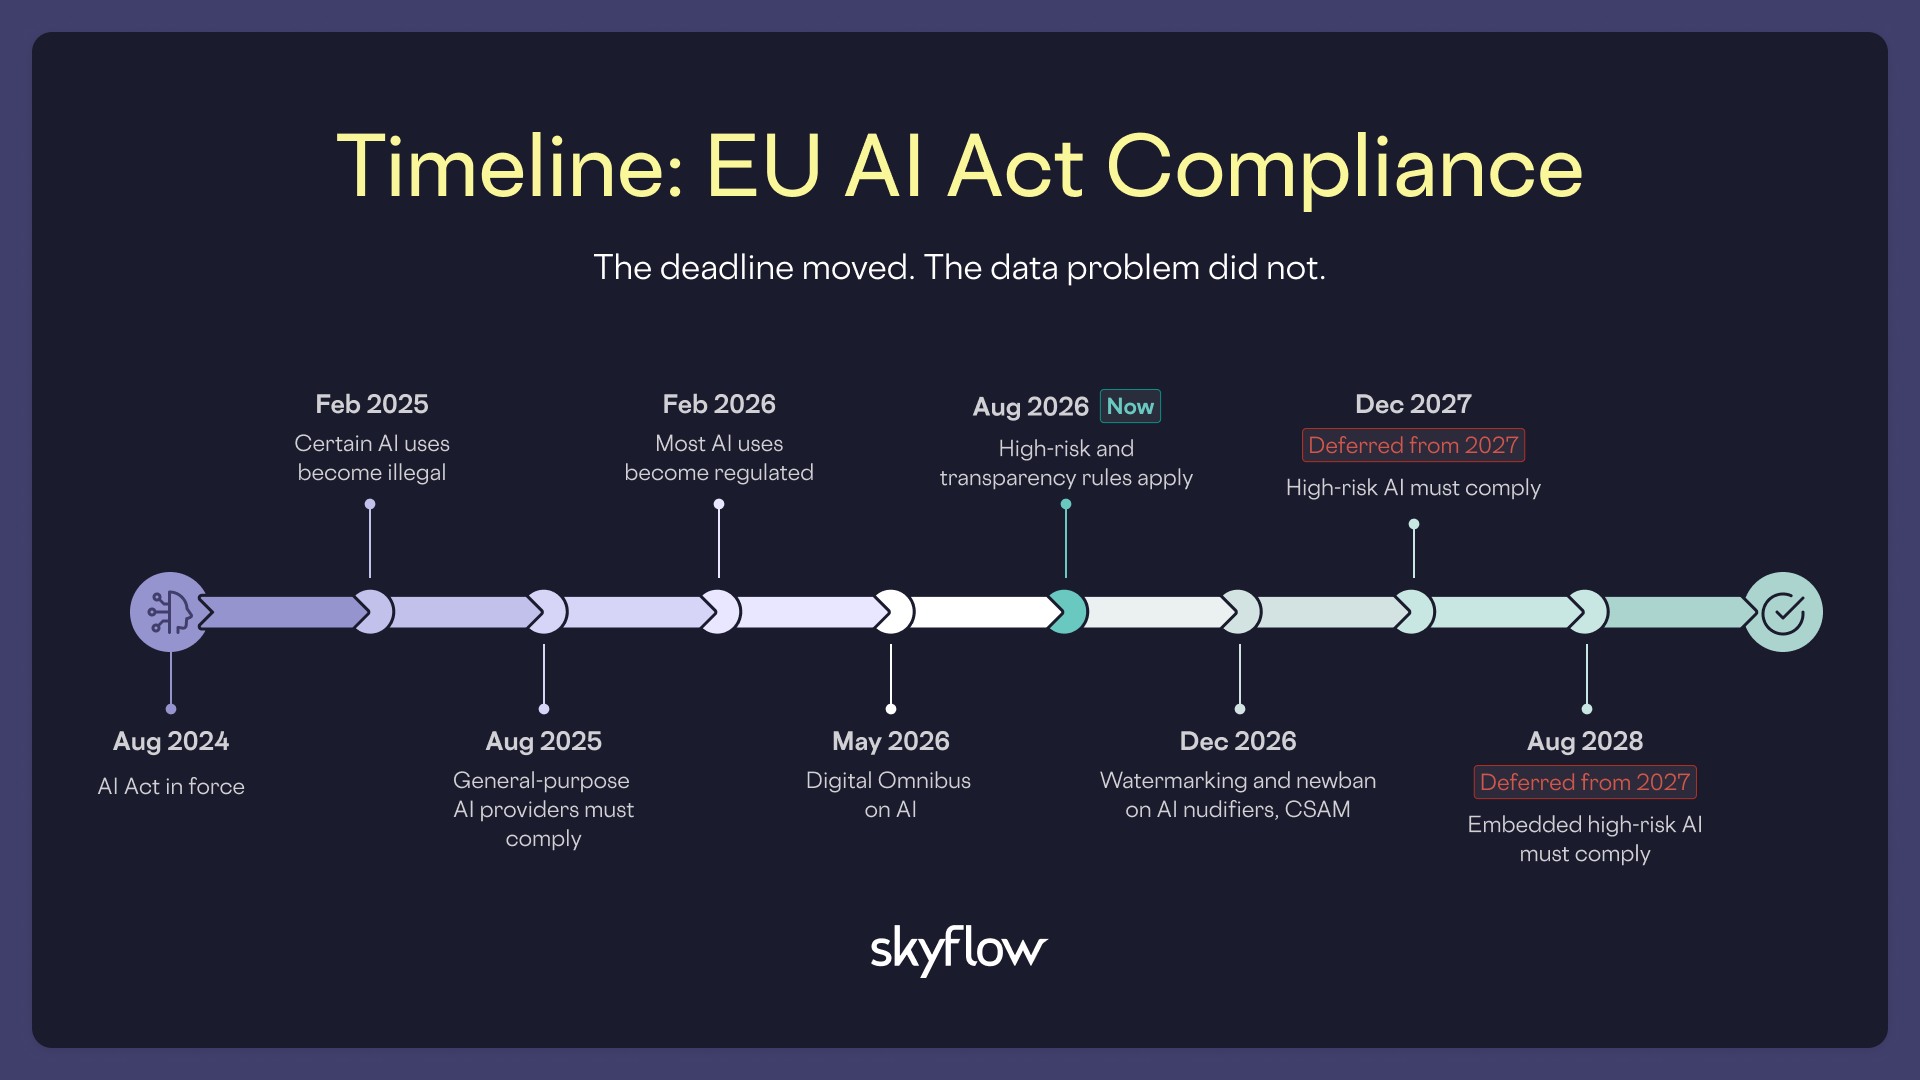
- How to layer this into an AI stack already in production, aligned with the EU AI Act
The model gets the right answer. The PII never leaves the data layer.
Complete the form below to register
What will you learn?
Why perimeter, cloud, and vault controls fall short once agents, not humans, are the ones touching data across prompts, models, MCP servers, and logs
How detection, protection, and governance at runtime keep PII out of AI systems without breaking accuracy or usability
What compliance by design looks like in practice, with live demos across prompts, unstructured documents, and enterprise search
"We were running on Skyflow in just hours, rather than the months it would take to build and implement even a fraction of this data privacy rigor"


TRUSTED BY

Learn More About Skyflow

Ready to Get Started?
Let us show you why Skyflow is the better way — sign up to talk to an expert today.